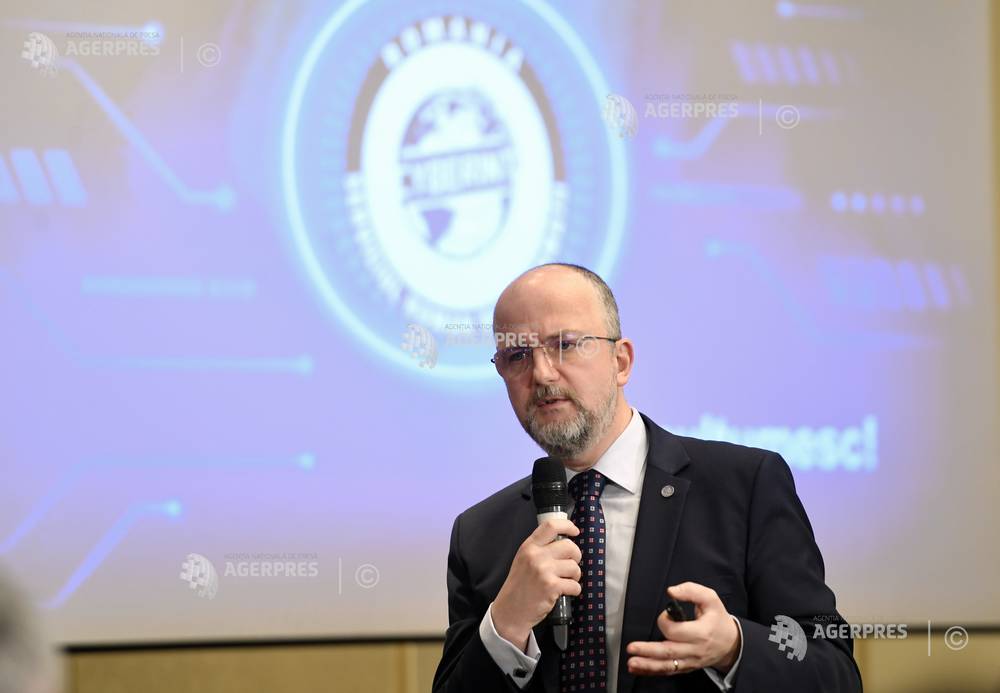
Romania's National Cyberint Centre has sent 1,304 notifications to various public institutions since 2021 concerning technical, procedural or human-related IT vulnerabilities within their systems, CNC head Anton Rog told a meeting of Parliament's information technology committees.
The committees examined the 14 July 2026 cyberattack on the National Agency for Cadastre and Land Registration (ANCPI), which disabled the e-Terra platform and halted real-estate transactions in Romania for almost a month.
The CNC head said warnings about compromises and critical vulnerabilities at ANCPI had been issued as early as 2021, adding that data held by the Romanian Intelligence Service (SRI) showed that there had been no official response from the agency.
'Specific investigations conducted by the National Cyberint Centre identified compromises and critical vulnerabilities as early as 2021, and these were communicated to the prime minister at the time and to the leadership of the Ministry of Development, Public Works and Administration and ANCPI. I would also like to point out that in 2025 alone we sent 233 notifications concerning vulnerabilities, not only to ANCPI but across the government sector in general, while between 2021 and 2026 we sent 1,304 notifications to various government institutions regarding technical, procedural or human-related vulnerabilities within their systems,' Rog said.
He said the attack on ANCPI was a ransomware attack carried out by the cyber threat actor ByteToBreach, adding that the attacker deleted approximately 1,000 virtual servers from the agency's network.
According to Rog, the cyberattack was made possible by several cybersecurity weaknesses, including the use of weak passwords that had also been reused over long periods, including for administrator accounts; old systems that had not been updated for several years; and permissive access rules within the institution's internal network.
Ionut-Andrei Iacoboaei, deputy director of Romania's National Cyber Security Directorate (DNSC), said ANCPI had used the same administrator password for different accounts, noting that this was not recommended practice.
'The escalation and compromise were made possible by a combination of factors - vulnerable systems, a lack of security updates and the use of the same passwords for different accounts. (...) From the DNSC's perspective, this was not a highly sophisticated attack; it was carried out by exploiting known vulnerabilities,' he said.
The National Cyber Security Directorate has sent notifications to 2,400 national-level public institutions identifying more than 40,000 vulnerabilities.
ANCPI representatives said the operations of the National Agency for Cadastre and Land Registration, affected by the 14 July cyberattack, could be fully restored next week.
'We are trying to take the best measures. Some of the applications have been restarted and I believe that, by next week at the latest, we will have fully resumed operations,' said ANCPI deputy director-general Mircea Popa.
Eduard Gheorghe, head of ANCPI's IT department, said there was no information indicating that the databases had been affected.
Radu Mihaiu, chairman of the IT Committee in the Chamber of Deputies, said the analysis showed that Romania's public institutions were not adequately protected and that more than a hundred of them could find themselves in the same situation as the Cadastre Agency at any time.
'Today's discussions have confirmed to me that the questions we must now ask are how many other institutions could find themselves in ANCPI's situation and, above all, when. We have a major problem. There are technical errors, but even more serious are the institutional failures that allow and even facilitate such attacks. There are components that are not covered by maintenance contracts and there are obsolete components that are obviously riddled with vulnerabilities. All this is because, at the management level of these institutions, there is no awareness of the real danger posed by cyberattacks. The reality is that Romania's institutions are not protected and that we have dozens, perhaps even hundreds, of institutions that could find themselves in ANCPI's situation at any time,' USR MP Radu Mihaiu said.
PSD Senator Marius Humelnicu said it was inexplicable that ANCPI had received specific warnings and had failed to act.
'I don't understand why you don't work with specialists. I believe the ANCPI president should be held accountable for what happened. I don't know why he hasn't resigned or been dismissed,' Humelnicu said. AGERPRES (RO - writing by: Alina Novaceanu; EN - writing by: Simona Iacob)
- Category: English
- Date: 2026-09-09 19:44:58
- Foto: Cristian NISTOR / AGERPRES Photo